
FOCTOS: security testing that keeps pace with your releases
Most organizations test their applications for security once or twice a year, but their software changes every week. Each release between two tests can carry a new weakness to customers before anyone has checked it. For a bank or a public service, that gap is where breaches, regulatory findings and headlines come from.
FOCTOS, a Snipeyes company, is built to close that gap. It tests your web applications and APIs (the connections your apps use to exchange data) continuously, and it proves which weaknesses are real before they reach your team.
What FOCTOS does for your organization
A penetration test is an authorized, controlled attack that finds weaknesses before criminals do. Skilled people carry it out, which makes it thorough but occasional. FOCTOS applies the same approach all the time. Its AI agents map your applications, look for weaknesses, then try to exploit them safely to show whether an attacker could really use them.
Anything serious is checked by a senior Snipeyes tester before it reaches you. Your engineers get a short list of confirmed problems, each with proof and fix guidance. Your leadership gets a plain summary of what is exposed and what it would mean for the business.
How it compares with what you may use today
| Vulnerability scanner | Annual manual penetration test | FOCTOS | |
|---|---|---|---|
| How often | On demand or weekly | Once a year | Continuously, as you release |
| What you receive | Long lists of possible issues, many false alarms | Deep findings from one point in time | Confirmed weaknesses, explained in business terms |
| Links weaknesses together | No | Yes, by hand | Yes, the AI proposes and a person confirms |
| Audit evidence | Raw export | Formal report after the engagement | Executive and technical reports mapped to standards |
| Fits developer tools | Bulk tickets | PDF handover | Jira, GitLab and GitHub, with suggested fixes |
The third row matters most. Real attacks often combine two or three small weaknesses into one serious breach. A common example is a flaw that shows another customer’s records, which is then used to take over that customer’s account. A scanner reports each piece on its own and misses the chain. FOCTOS looks for the chain and tests it.
What your security and engineering teams receive
- Proof for every critical finding: a proof of concept (a safe demonstration that the attack works), with screenshots or logs and severity scores based on CVSS and the OWASP Risk Rating.
- A risk score that weighs how easy an attack is against what it would expose, such as customer accounts, funds or personal data.
- A one-page executive summary, backed by a full technical appendix.
- A mapping of each finding to ISO/IEC 27001:2022, SOC 2, PCI DSS 4.0 (requirements 11.3 and 11.4), GDPR Article 32, NIST CSF and OWASP ASVS.
- Connections to GitLab, Jenkins, GitHub Actions, API gateways and Jira. FOCTOS suggests the code change for each fix and holds back a release only when a critical finding is confirmed.
How a test runs
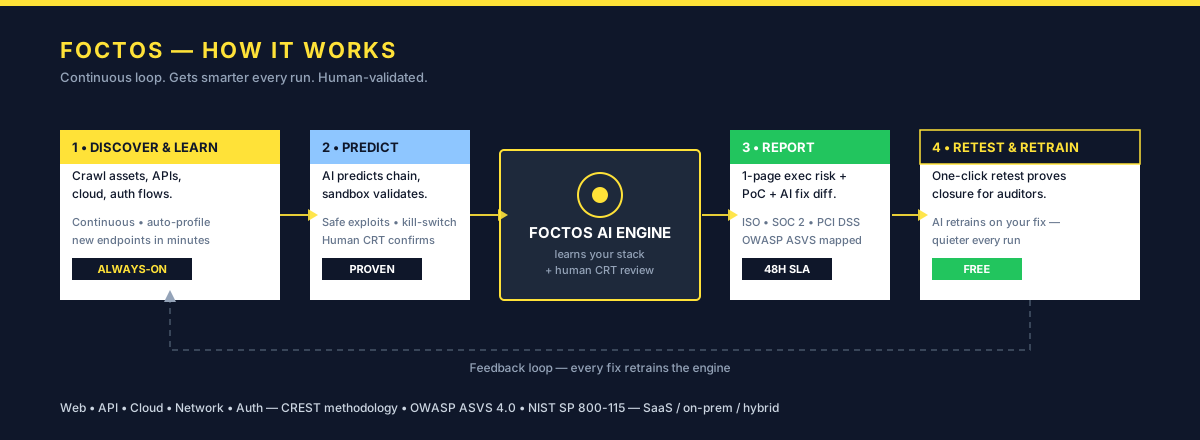
- Discover: FOCTOS maps your applications, APIs and cloud environments on AWS, Google Cloud and Azure, and learns how your logins work. New endpoints are added to the map as they appear.
- Predict and prove: It picks the attack paths with the highest impact and tests them safely, at a controlled rate. A senior Snipeyes tester confirms the result. Testing can be stopped at any moment.
- Report: You receive the executive summary, the technical evidence, suggested fixes and the compliance mapping.
- Retest: Once a fix is in place, a retest confirms the issue is closed. This is included, and it is the evidence auditors usually ask for. Each fix also teaches the system, so false alarms become rarer over time.
What it covers and where it runs
FOCTOS tests web applications, APIs (REST and GraphQL), mobile app backends, external and internal networks, cloud configuration (IAM, storage buckets and Kubernetes) and login systems (SSO, OAuth and JWT). You can run it as a cloud service, on your own premises or as a mix of the two, in more than one region. Access is controlled with single sign-on, role-based permissions and audit logging, managed per group of assets.
Behind the scenes, FOCTOS coordinates several leading AI models and agent frameworks. Our team benchmarks and supervises them, so each task runs on the model best suited to it. Your data is covered by an NDA, can stay in your region, and personal data is kept to a minimum. Model governance is aligned to ISO/IEC 27001 and ISO/IEC 42001.
Who uses it alongside what
FOCTOS suits banks, fintechs and software companies that release often, where a year between tests is simply too long. It works well next to our manual VAPT (vulnerability assessment and penetration testing), which remains the right tool for the annual deep review. Enterprises and security providers can find integrations and partnership options at foctos.com.
See FOCTOS at foctos.com
Explore the platform, or ask for a demo on one of your own applications.
Cloud, on-premises or hybrid • Staging-first testing available