Cybersecurity Assurance: evidence your board and auditors can rely on
Boards tend to ask their security leaders the same questions. Could we withstand a real attack? Will we pass the audit? Where should the next budget go? Assurance means answering those questions with test results instead of assumptions. Our testing is carried out by CREST-certified testers from a CREST-accredited, ISO/IEC 27001:2022-certified company.
What the organization gains
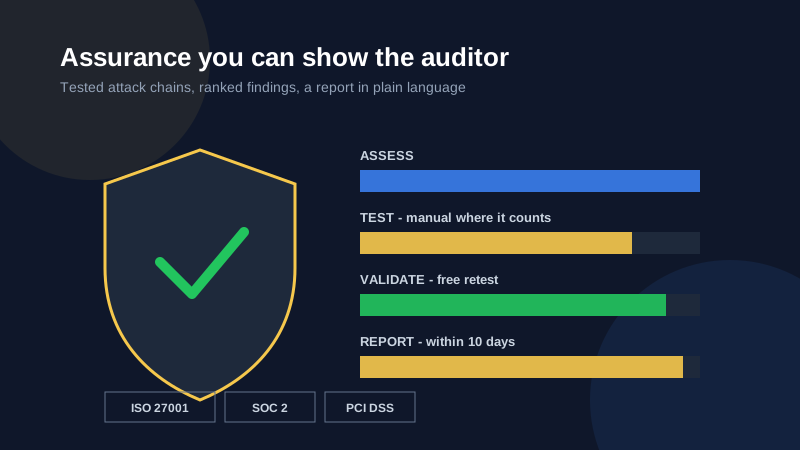
The main gain is evidence. Findings are mapped to ISO/IEC 27001:2022, SOC 2, PCI DSS and what regulators expect, so the same work supports your audits.
Each finding is also ranked by how easily it could be exploited, and comes with an attack narrative explaining how an attacker would chain the steps together. That makes it much easier to decide where remediation money should go. Once fixes are in, a retest (included in the price) confirms which findings are closed, so progress can be reported with facts.
Services in the programme
- Penetration testing, where experts attack your external and internal networks, APIs, cloud and mobile apps under controlled conditions. It follows PTES, NIST SP 800-115 and OWASP WSTG, and the manual work concentrates on chained attack paths.
- Red team exercises: a realistic simulated attack across people, processes and technology, mapped to MITRE ATT&CK, that measures how quickly your security team notices and responds.
- Vulnerability management, meaning regular automated checks for known weaknesses, with false alarms removed and findings turned into tickets your engineers can act on.
- Source code review, combining automated scanning with expert review of your code against OWASP ASVS to find logic flaws that tools cannot see.
- Social engineering tests, such as simulated phishing, that show who clicks, who reports, which groups are most exposed and what training would help.
What each engagement delivers
Every engagement ends with a report within 10 days of testing. It contains an executive summary for leadership and full technical findings rated with CVSS, the standard 0 to 10 severity scale. All work is covered by a non-disclosure agreement (NDA).
Compliance mapping
| Framework | What our testing supports |
|---|---|
| ISO 27001:2022 | Evidence that controls have been tested |
| SOC 2 | Validation against the Trust Services Criteria |
| PCI DSS | Support for Requirement 11 security testing |
| NIST CSF | Coverage of Identify, Protect and Detect |
Where to start
We begin with a scoping workshop to agree what will be tested, the rules of engagement and a fixed price. Get in touch and you will have a scoped proposal within 24 hours. Talk to our team.