Secure Software Development: fast releases with security built in
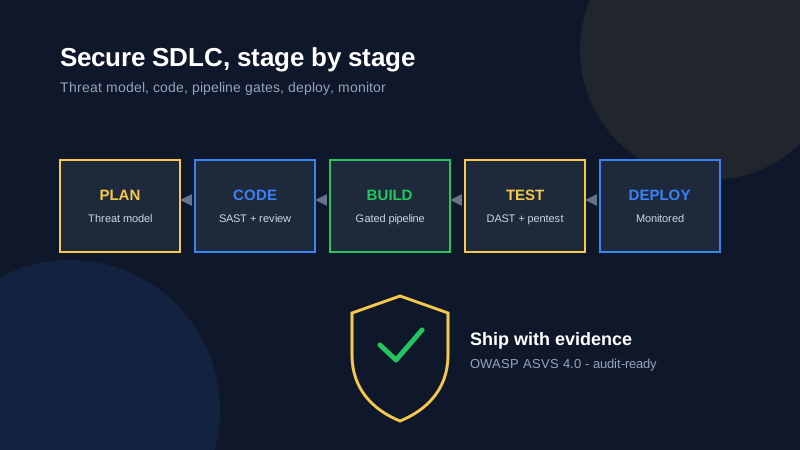
Flaws in applications are a common way for attackers to get in, and a flaw fixed in production costs far more than one caught at the design stage. A secure software development life cycle (secure SDLC) builds security checks into every stage of how software is planned, written and released. Your teams keep their release pace, and each release comes with evidence your auditors can review.
What improves
Fewer security problems reach production, because vulnerabilities are caught at design, commit and build time. Audit preparation gets easier, because an OWASP ASVS evidence pack supports ISO/IEC 27001:2022, SOC 2 and enterprise customer security reviews. Development speed holds up as well. The checks run inside your pipeline and give developers fix guidance at the moment they need it.
What we put in place
- Threat modeling and secure design review. In STRIDE-based workshops for each major feature (STRIDE is a structured way of listing what could go wrong), risks are recorded before any code is written.
- Code assurance, with SAST and SCA tuned to your technology, plus expert manual review for the logic flaws that tools miss.
- Pipeline checks: SAST, DAST, SCA and secret scanning wired into GitLab, GitHub or Jenkins, with quick feedback to the developer.
- Container and infrastructure-as-code hardening, including image baselines, Kubernetes and Terraform checks against CIS Benchmarks, and monitoring of third-party dependencies.
- Developer enablement through secure coding coaching and playbooks, so your team relies on us less over time.
Compliance mapping
| Framework | What we provide |
|---|---|
| OWASP ASVS | Verification level evidence for each release |
| NIST SSDF | Evidence of secure development practices |
| ISO 27001:2022 | Evidence for Annex A 8.25-8.29 (secure development) |
Ways to work with us
| Model | Suited to | Typical duration |
|---|---|---|
| Embedded AppSec squad | Teams releasing continuously | Quarterly |
| Pipeline uplift | Pipelines with no security checks yet | 4-6 weeks |
| Assessment and roadmap | Planning the next financial year | 2-3 weeks |
Getting started
A scoping workshop maps your technology, your main risks and the smallest useful first step. Talk to our team and we will follow up with a scoped proposal within 24 hours.