Accreditations & Certifications

CREST accredits our penetration testing. ISO/IEC 27001:2022 certifies how we protect your information.

CREST Accredited Member - Penetration Testing ISO/IEC 27001:2022 Certified - Information Security Management

Some of the organizations we work with

  • Banking
  • Insurance
  • Capital markets
  • Fintech
  • Transport & logistics
  • Mining
  • Technology
  • MIND ID
  • Amar Bank
  • Bank Syariah Indonesia
  • Bank BTN
  • Thales
  • PFI Mega Life
  • DBS Indonesia
  • Superbank
  • Hibank
  • Sinarmas Sekuritas
  • KAI Commuter
  • EDII (IPC group)
  • IST
  • Antam
  • Link Net
  • Adapundi
CREST-accredited ISO/IEC 27001:2022 certified

A clean scan report can give your board false comfort

Automated scanners catch known, surface-level issues. The weaknesses behind fraud and regulatory findings usually sit in the business logic, such as a flaw that lets one customer open another customer's account. Our testers find these by hand and confirm each one can actually be exploited before it reaches your report. Findings are ranked by business impact, so budget and effort go to the risks that matter most.

We follow published methods such as OWASP, PTES and NIST SP 800-115, so every finding can be independently verified and repeated.

Find the weaknesses that matter

Manual penetration testing and red teaming, which is a longer, quieter simulated attack. We show how small flaws combine into real harm, so you know what to fix first.

See how we test

Build new systems safely

We work with your developers from the design stage. Security checks then run automatically every time the code changes, and releases stay on schedule.

Secure development

Keep watch once it is live

Our analysts monitor your systems at all hours. If an attack starts, we help you contain it and tell you exactly what needs fixing.

Managed monitoring

How an engagement works

Request a Briefing

What we found, and how it was fixed

See all case studies

By industry

All industries

Latest insights

More insights

Questions leaders ask us

How long does a penetration test take?

It depends on the scope: how many systems, applications and APIs are in it, and whether we test from outside or inside your network. We agree the scope with you before any work starts, and the proposal states the testing window. It also shows when you receive the report.

What is the difference between a vulnerability assessment and a penetration test?

A vulnerability assessment uses scanners to list known weaknesses across many systems. A penetration test goes further: testers try to exploit weaknesses by hand, chain them together and show what an attacker could actually reach. Read the full comparison

Will our auditor accept the report?

That decision stays with your auditor. We map each finding to ISO/IEC 27001:2022, SOC 2, PCI DSS 4.0, OWASP ASVS and your regulator's rules, so the evidence lines up with the controls they check. What auditors look for

Is CREST a testing standard?

No. CREST is an accreditation and certification body. Snipeyes is a CREST Member, and our testers follow published methods such as OWASP, PTES and NIST SP 800-115.

Do you cover regulator requirements in Indonesia?

Yes. Findings can be mapped to the rules your regulator applies, such as OJK and Bank Indonesia regulations for banks. Which rules apply depends on your license, so we confirm them during scoping. Banking and financial services

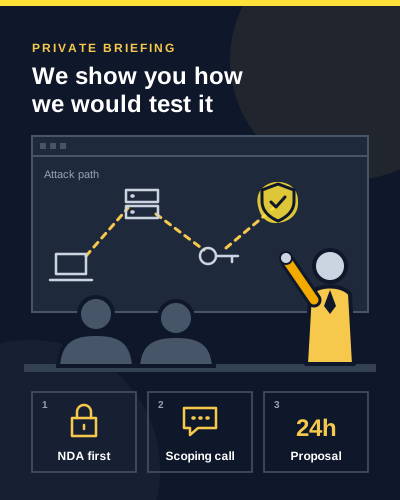
Illustration of a Snipeyes consultant walking client leaders through an attack path, then three steps: NDA first, scoping call, proposal in 24 hours

Request a Briefing

Tell us what is on your mind: an audit coming up, a new system about to go live, or an incident you want to understand. One of our principal consultants will walk your leadership through how we would test it and what you would receive. The steps above show what happens next.

Prefer to pick a time? Book a call directly.

Business Inquiry
Order Details

Everything you send us stays confidential. We use these details only to reply to your request. Read our privacy policy.


Chat on WhatsApp